Request-side leakage
Sensitive materials or credentials leave with context.
Define checkpoints along model requests and tool execution, gradually integrating existing applications and agents.
Control what may be accessed and sent.
Keep tool calls within permissions and approvals.
Link events with identities, tasks and policy decisions.
Break risk into concrete stages to determine what must be integrated and who is responsible.
Sensitive materials or credentials leave with context.
Processing nodes may access or change content; clarify paths and sources.
Returned content may steer commands or tool parameters away from business objectives.
Agents may request actions beyond task permissions.
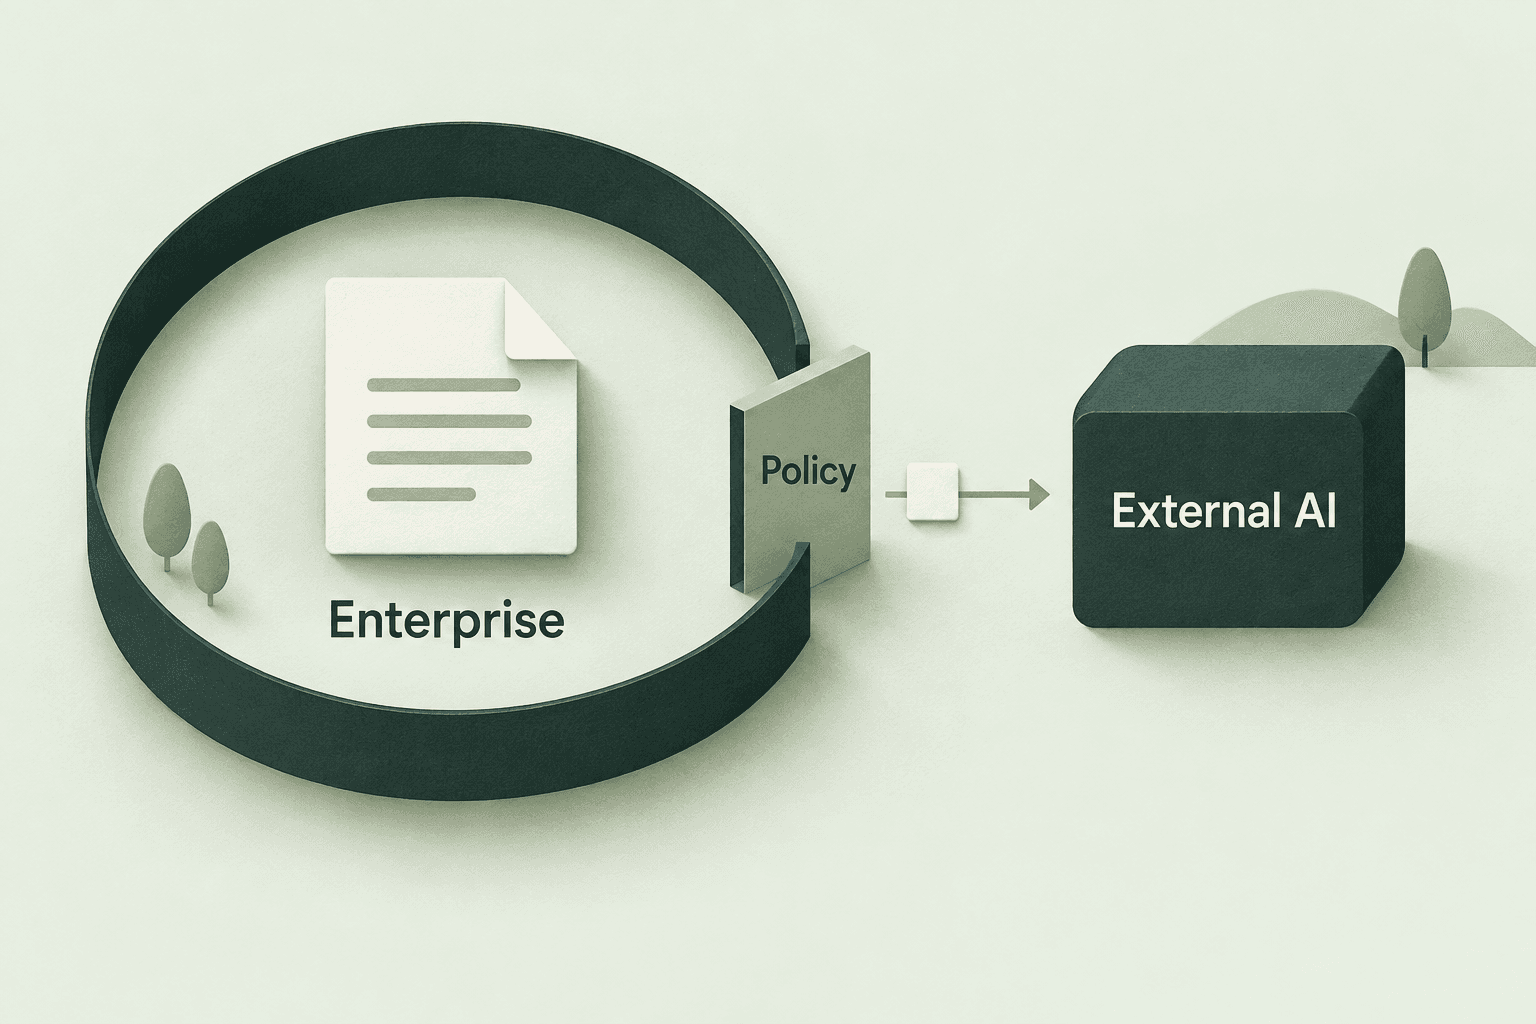
Use Route Fence at control points, with identity-based access, resource tests and controlled workflows.
Policies for data checks, model access and tool execution.
Unified model access, application identity and permissions.
Evidence on resource performance and anomalous signals.
Organize digital-worker tasks and run controlled workflows within the integrated scope.
For each integration, define who processes data, who accesses credentials and what logs contain.
Define responsibilities between intranet or VPC gateways and external management services.
Confirm where keys are stored, used, accessed and rotated.
List controlled tools and unintegrated paths to avoid misunderstandings about coverage.
Retain metadata, masked sensitive content and approval records as required.
When an unauthorized tool action appears, block or request approval, notify the owner, link evidence and review rules and coverage.
Integrated execution endpoints match rules and record rejected or pending-approval status.
Link tasks, identities, action parameters and policy versions.
Owners approve rule updates, followed by validation in a test scope.
Provide model entry points, agents, tools and sensitive-data categories to establish scope first.